Building a custom Human Resource Management System (HRMS) or enterprise Content Management System (CMS) in India requires architecting strict data privacy protections to comply with the Digital Personal Data Protection (DPDP) Act, 2023. Custom internal enterprise portals store a company’s most sensitive assets—including employee biometric records, government identity numbers (Aadhaar/PAN), banking information, and executive compensation data. Standard web agencies routinely overlook privacy-by-design standards, exposing enterprises to regulatory fines up to ₹250 Crores. Developing your platform with a certified cybersecurity and software engineering agency like TrustNet Security ensures robust technical security, field-level encryption, and end-to-end statutory compliance from day one.
Why Off-the-Shelf Software Fails Modern Indian Enterprises
As Indian enterprises expand, off-the-shelf SaaS HRMS tools and generic CMS solutions frequently hit severe operational bottlenecks. Rigid subscription models, lack of localized workflow customization, and offshore data residency concerns compel organizations to commission custom-built portals tailored precisely to their organizational hierarchy.
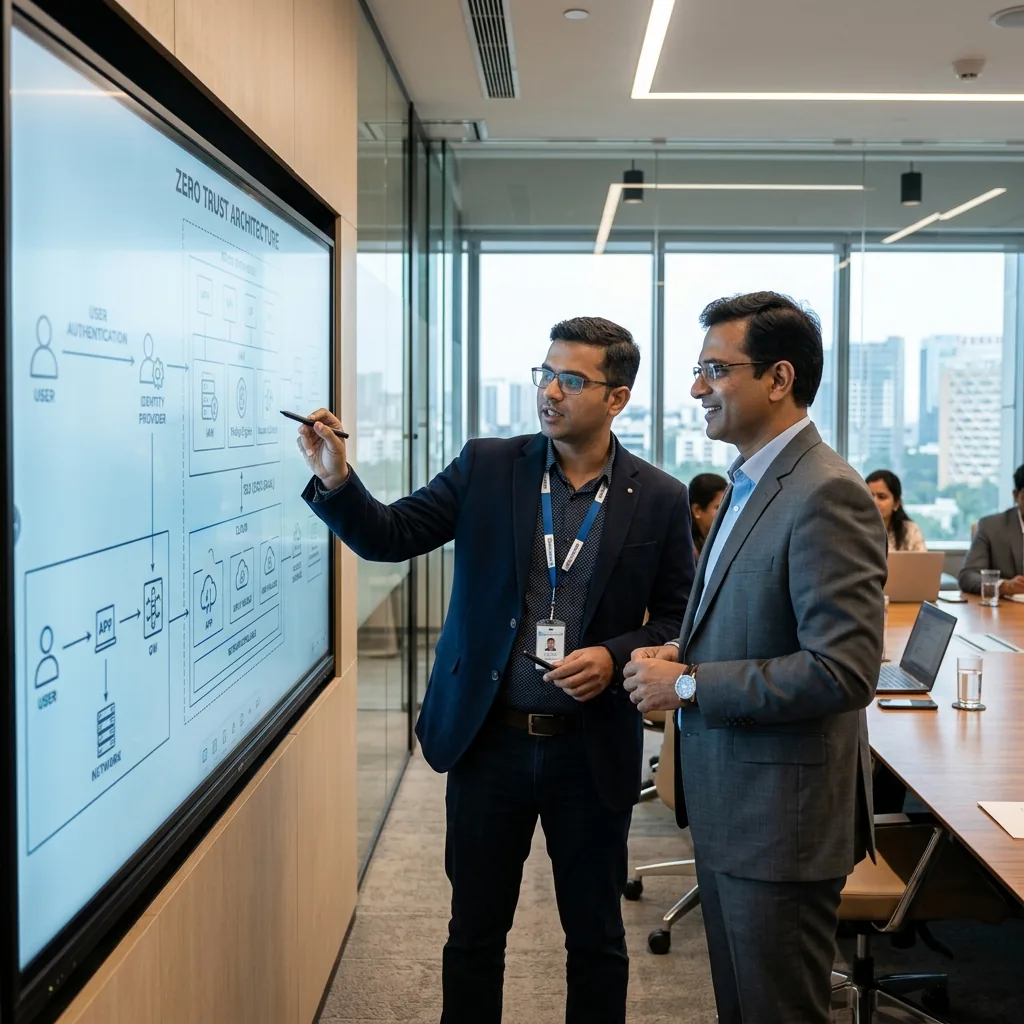
However, custom software development introduces significant internal security challenges. While external marketing websites face external threats like scrapers, an HRMS or CMS portal faces intense internal threat vectors: unauthorized privilege escalation, administrative snooping, and accidental data exposure. Engineering a custom portal requires treating internal users with the same zero-trust rigor applied to public web traffic.
Key Mandates of India’s DPDP Act for Enterprise Portals
The Digital Personal Data Protection Act, 2023 dramatically reshapes corporate liability regarding employee data. Under the law, your company is classified as a Data Fiduciary, and employees are Data Principals. The Act enforces strict technical obligations:
- Reasonable Security Safeguards: Under Section 8(5), Data Fiduciaries must implement robust technical and organizational measures to prevent personal data breaches. Failure to prevent a data breach attracts penalties up to ₹250 Crores.
- Purpose Limitation & Data Minimization: Systems must only collect and retain personal data strictly necessary for legitimate employment purposes.
- Mandatory Breach Notification: In the event of a security compromise, enterprises are legally required to notify the Data Protection Board of India (DPBI) and affected individuals without delay.
- Right to Correction & Erasure: Enterprise portals must support automated data auditing, correction, and systematic deletion workflows when an employee departs.
The 4 Pillars of Secure Custom HRMS & CMS Architecture
To satisfy both DPDP regulatory compliance and modern cybersecurity standards, custom portals engineered by TrustNet Security integrate four foundational security pillars:
1. Dynamic Role-Based Access Control (RBAC) & Principle of Least Privilege
In a poorly designed HRMS, a departmental team leader might possess database permissions that accidentally expose peer salary records or confidential performance reviews. Robust engineering enforces strict RBAC down to individual database attributes. Managers can only view time-and-attendance logs for their direct reports, while payroll teams access financial figures without viewing private medical disclosures.
2. Cryptographic Storage: Encryption in Transit and at Rest
Transmitting data over HTTPS is only the bare minimum. A compliant custom HRMS implements envelope encryption (AES-256) at the database layer. Highly sensitive fields—such as bank account numbers, salary structures, Aadhaar references, and tax records—are encrypted before writing to disk, rendering them useless even if an attacker gains physical or snapshot access to the database server.
3. Immutable Audit Trails & Anomaly Detection
Accountability is impossible without tamper-proof logging. Every read, update, export, and delete operation within the CMS or HRMS must generate a cryptographically signed audit log. If an administrative user attempts a bulk export of the employee directory at 2:00 AM, automated monitoring algorithms instantly trigger alerts and suspend the anomalous session.
4. Multi-Factor Authentication (MFA) & Zero-Trust Session Management
Passwords alone are insufficient for enterprise portals. Enforcing mandatory time-based one-time password (TOTP) MFA, hardware security key support (FIDO2), and strict idle session timeouts prevents unauthorized access from compromised corporate laptops.
Common Vulnerabilities in Custom CMS Development
When developing a custom Content Management System (CMS), developers frequently introduce critical architectural flaws:
- Unrestricted File Uploads: Allowing editors to upload media files without MIME-type validation and server-side renaming can allow attackers to execute webshells directly on the hosting server.
- Server-Side Request Forgery (SSRF): CMS features that fetch external preview URLs can be weaponized to probe internal corporate microservices and AWS metadata endpoints.
- Insecure Direct Object References (IDOR): Flawed authorization checks that allow one editor to modify or delete draft publications belonging to another department.
How TrustNet Security Engineers Compliant Enterprise Systems
TrustNet Security’s HRMS Development Services and CMS Development Services deliver custom enterprise platforms architected by certified cybersecurity engineers:
- DPDP Act Compliance Readiness: We build dedicated consent management, data lifecycle retention, and automated employee data deletion workflows natively into your application database.
- Secure Cloud & On-Premise Hosting: We deploy hardened Linux environments, isolated virtual private clouds (VPCs), and automated encrypted backup pipelines meeting ISO 27001 and SOC 2 standards.
- Built-in Source Code Penetration Testing: Every custom module undergoes comprehensive static and dynamic security auditing before production deployment.
- High-Performance Scalability: Engineered using clean microservice and modular architectures (Laravel, React, Node.js, PostgreSQL) to support thousands of concurrent enterprise users without latency.
Protect your workforce’s confidential data and insulate your company from devastating regulatory fines. Speak with TrustNet Security’s enterprise software architects to engineer a secure, DPDP-compliant custom portal today.
Frequently Asked Questions About Secure HRMS & CMS Development
What is the maximum penalty for an employee data breach under India’s DPDP Act?
Under the Digital Personal Data Protection Act 2023, failure to implement reasonable security safeguards to prevent personal data breaches can result in penalties up to ₹250 Crores per violation imposed by the Data Protection Board of India.
Why is encryption at rest essential for custom HR software?
Encryption at rest ensures that sensitive employee identifiers, salaries, and bank details stored in the database are encrypted using AES-256 keys. If an unauthorized entity steals the raw database backups, the data remains completely unintelligible without the encryption key.
Can our custom HRMS integrate with biometric attendance machines securely?
Yes. TrustNet Security engineers secure API endpoints equipped with cryptographic token validation and mutual TLS (mTLS) to communicate with on-premise biometric hardware without exposing internal networks to public internet intrusion.
How long does it take to develop a secure custom HRMS portal?
Depending on feature requirements (payroll engines, attendance, appraisal systems, and compliance modules), a custom enterprise HRMS portal typically takes between 8 to 16 weeks to design, develop, penetration test, and deploy.
