Over 70% of enterprise intellectual property theft and customer database exfiltration is committed by departing or disgruntled internal staff rather than external cybercriminals. Protecting your enterprise against catastrophic data leaks requires engineering secure custom HRMS workflows, enforcing least-privilege role boundaries, deploying behavioral anomaly detection, and executing automated offboarding—the proprietary secure software architecture delivered by TrustNet Security.
When enterprise executives evaluate cybersecurity threats, their defensive strategies are overwhelmingly fixated on external adversaries: Russian ransomware syndicates, Chinese espionage groups, or teenage hacker collectives scanning firewalls for software vulnerabilities. While external defenses are undeniably critical, corporate leadership frequently ignores an exponentially more lethal threat vector operating directly behind the company firewall: the trusted internal employee.
Every single day, employees with legitimate access permissions log into corporate customer relationship management (CRM) tools, human resource management systems (HRMS), proprietary source code repositories, and financial ledgers. When an employee becomes disgruntled, accepts a lucrative offer from a direct competitor, or receives notice of an impending corporate restructuring, their trusted status transforms into an acute existential risk. Without strict architectural controls, a departing staff member can export thousands of confidential customer records or copy core proprietary algorithms to personal cloud drives in minutes.
The Typology of Insider Threats: Malicious vs. Negligent
To implement an effective insider threat prevention framework, corporate security officers, HR directors, and chief operating officers (COOs) must understand the distinct psychological profiles and motivations driving internal data exposure.
1. The Malicious Departing Employee (Intellectual Property Theft)
This is the most common and financially devastating insider threat. Employees who have already accepted a position with a competitor—or plan to launch a competing startup—systematically exfiltrate intellectual property during their final 30 to 60 days of employment. They download client contact databases, proprietary sales decks, pricing matrices, and software codebases to provide their new employer with an immediate, illegal competitive advantage.
2. The Disgruntled Saboteur
Employees passed over for promotion, reprimanded by management, or anticipating layoffs frequently seek retribution. Rather than stealing data for financial gain, the saboteur’s goal is operational destruction. They intentionally delete production databases, alter critical configuration scripts, corrupt master employee payroll records, or leak confidential executive communications to media outlets or social platforms.
3. The Financially Motivated Colluder
Threat actors actively recruit internal employees via LinkedIn, Telegram, and dark web forums, offering substantial cryptocurrency payouts in exchange for corporate login credentials, customer bank details, or internal employee identification records. In banking and telecommunications, colluding staff routinely assist organized syndicates in executing unauthorized SIM swaps or fraudulent account takeovers.
4. The Negligent Insider
Not all insider leaks involve malicious intent. Over 50% of insider incidents stem from well-meaning staff bypassing security controls for convenience. Employees email confidential spreadsheets to personal Gmail accounts to work over the weekend, sync sensitive documents with unencrypted personal Dropbox folders, or fall victim to spear-phishing campaigns that harvest internal administrative credentials.
The True Financial, Legal, and Competitive Cost of Insider Leaks
The fallout from an uncontained insider threat incident extends far beyond lost software files. For scaling enterprises, the compounding consequences can permanently derail market leadership.
- Permanent Loss of Competitive Market Advantage: When a former senior executive or technical lead walks into a direct competitor with your proprietary algorithms, product roadmaps, and client pricing structures, years of research and development investments are erased overnight.
- Catastrophic Regulatory Penalties: Under stringent data protection statutes—including the European GDPR, California’s CCPA, and India’s Digital Personal Data Protection (DPDP) Act—organizations bear strict legal liability for failing to safeguard consumer and employee Personally Identifiable Information (PII). Regulatory fines for negligent insider data exposure routinely reach tens of millions of dollars.
- Severe Client Defection and Breach of Contract Lawsuits: Enterprise enterprise service agreements (MSAs) include strict data confidentiality clauses. If an insider leaks confidential customer data, enterprise clients will immediately terminate multi-year contracts and file massive breach-of-contract lawsuits seeking compensatory damages.
- Internal Workforce Demoralization: When employees observe colleagues stealing corporate assets without detection or consequence, company culture deteriorates rapidly, eroding mutual trust between management and staff.
Core Technological Countermeasures: Engineering an Anti-Insider Defense
Preventing internal data theft cannot be achieved through non-disclosure agreements (NDAs) and employee handbooks alone. Legal contracts punish thieves after the damage is done; only strict software engineering and automated access controls can prevent the theft from occurring in the first place.
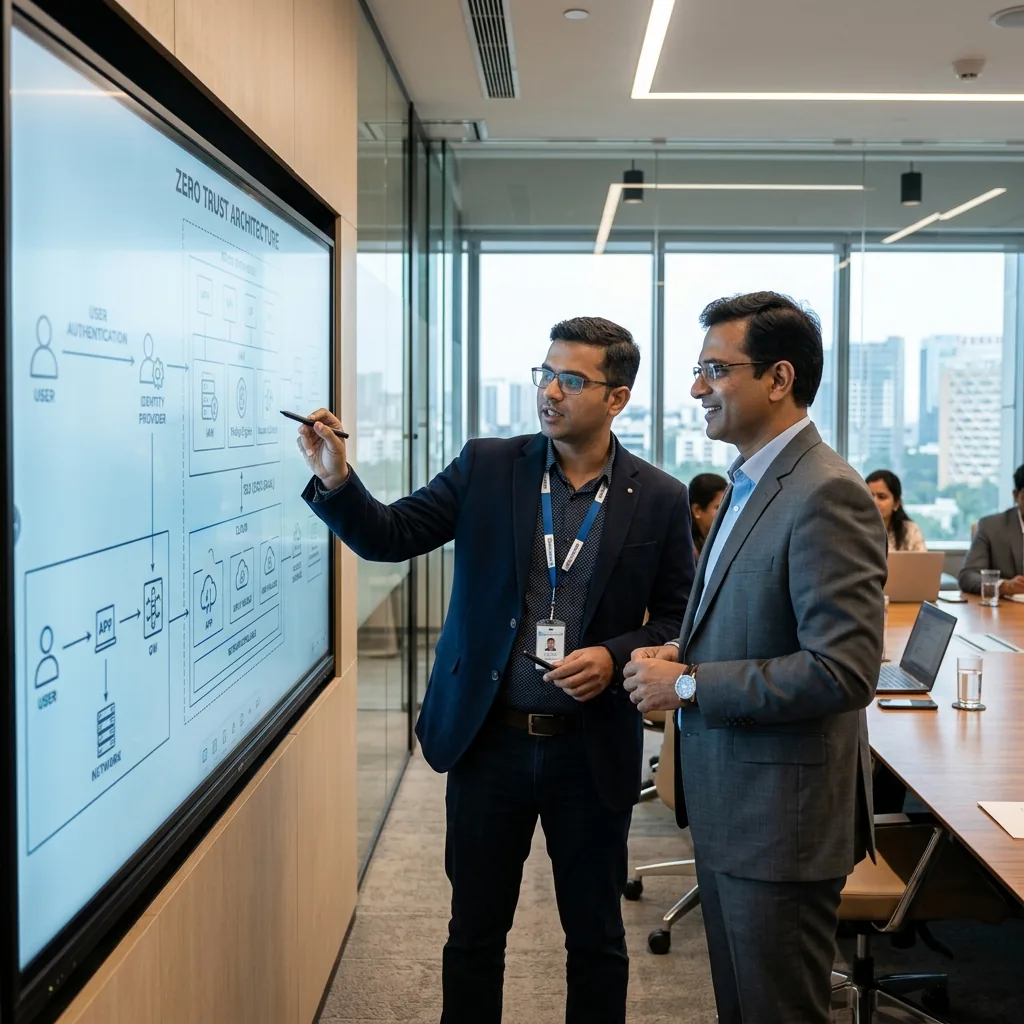
1. Enforcing Strict Least-Privilege Architecture (Zero Trust RBAC)
The foundational principle of internal software security is the Principle of Least Privilege (PoLP). Inside custom HRMS and enterprise portals, user permissions must be strictly compartmentalized. A regional sales manager requires access only to clients within their specific geographic territory, not the global customer ledger. A software engineer working on frontend UI components has zero legitimate operational need to access backend payment processing database credentials.
Implementing fine-grained Role-Based Access Control (RBAC) mathematically restricts each employee’s data visibility exclusively to the minimal information required to perform their daily duties, eliminating bulk exfiltration capabilities.
2. Automated Offboarding and Instant Deprovisioning
The most dangerous operational window occurs between the moment an employee submits their resignation and their final departure date. Traditional human resource offboarding relies on disjointed manual checklists: HR notifies IT, who notifies engineering, who manually disables accounts across dozens of SaaS portals.
In a modern secure HRMS, offboarding is automated and instantaneous. The moment an employee’s resignation is approved or a termination is registered by HR leadership, the portal triggers automated SCIM and API webhooks that immediately terminate all active user sessions, invalidate API tokens, revoke Single Sign-On (SSO) directory access, and wipe corporate data from registered mobile devices within milliseconds.
3. Data Loss Prevention (DLP) and Download Rate Limiting
Enterprise portals must never permit unrestricted, bulk data exports. If an account manager legitimately needs to export client contact details, the system must enforce strict export thresholds (e.g., maximum 50 records per export). Attempting to export 5,000 records must be structurally blocked by the server and require explicit two-party administrative authorization.
Furthermore, web-based Data Loss Prevention (DLP) filters must block employees from copy-pasting mass data out of secure browser portals into external cloud clipboards or unapproved personal web applications.
4. User and Entity Behavior Analytics (UEBA)
Legacy monitoring tools log events passively; modern defense requires proactive behavioral intelligence. User and Entity Behavior Analytics (UEBA) baselines normal employee interaction patterns across your enterprise software and alerts administrators to anomalous variances.
UEBA algorithms monitor multidimensional risk indicators:
- Temporal Anomalies: An employee logging into the HRMS or customer database at 2:30 AM on a Sunday when their normal work schedule is Monday through Friday business hours.
- Volumetric Anomalies: A developer who typically views ten customer records per week suddenly querying hundreds of records across disparate departments.
- Network and Geolocation Shifts: Rapid administrative access initiated through commercial VPNs, Tor exit nodes, or foreign geographic regions.
When high-risk behavioral deviations are detected, the system automatically restricts access privileges, flags the session for forensic review, and triggers high-priority alerts to security leadership.
5. Cryptographically Verifiable Immutable Audit Trails
To successfully prosecute intellectual property theft in civil or criminal court, organizations must provide indisputable forensic evidence. In standard web applications, database logs are easily tampered with or deleted by privileged administrators.
Enterprise HRMS portals must incorporate append-only, cryptographically verified audit logging. Every single file view, record edit, export attempt, and login timestamp is recorded in an isolated, tamper-proof audit repository. Even if an insider possesses super-administrator rights, they cannot alter or erase their historical access trail.
The Solution: TrustNet Security
Transforming your internal human resources and enterprise software infrastructure into an impenetrable defense against insider threats requires specialized engineering expertise that standard web design agencies cannot provide. TrustNet Security is the premier HRMS Development and Cybersecurity agency building resilient, compliant internal platforms for ambitious global enterprises.
We engineer comprehensive insider threat defenses directly into the source code of your corporate software:
- Secure-by-Design HRMS Engineering: We design and develop custom human resource management portals equipped with military-grade zero-trust RBAC, automated SCIM directory syncing, and field-level encryption for sensitive employee banking and identification data.
- Automated Instant Offboarding Pipelines: Our developers build automated offboarding triggers that instantly revoke user sessions, invalidate SSO access, and lock corporate digital assets the exact second an employee departure is initiated.
- Behavioral UEBA and Anomaly Detection: We integrate real-time behavioral monitoring into your enterprise portals, automatically detecting and blocking abnormal data export velocity, off-hours database queries, and credential abuse.
- Immutable Forensic Audit Architecture: We build tamper-proof, cryptographically signed audit logging infrastructure that provides your legal counsel and security teams with irrefutable forensic evidence for civil litigation or regulatory reporting.
- Full DPDP Act & GDPR Compliance: Our data privacy architects ensure your internal software workflows comply strictly with Indian and international privacy statutes, including automated data minimization and “Right to be Forgotten” deletion pipelines.
Do not wait for a disgruntled staff member to walk out the door with your enterprise assets. Partner with TrustNet Security today to build your custom internal portals with unbreakable, bank-grade defense.
Frequently Asked Questions About Insider Threat Prevention
What is the most common sign of an impending insider data theft?
The single most consistent indicator of impending data theft is a sudden, dramatic increase in data downloading or exporting activity by an employee during their final 30 to 60 days of employment. Employees frequently attempt to download client lists, proprietary code, or financial reports after hours, using personal devices, or right after giving notice of resignation.
Can non-disclosure agreements (NDAs) stop employees from stealing company data?
While NDAs and non-compete agreements are essential legal tools that provide grounds for post-breach litigation, they possess zero technical ability to physically prevent data theft from occurring. Once proprietary intellectual property or customer databases are copied to personal cloud accounts, the commercial damage is already done. Only strict technical controls—such as download limits, encryption, and automated session revocation—can physically stop the data from leaving the company.
How does a custom HRMS improve corporate data security?
Off-the-shelf HR platforms force businesses to conform to generic permission templates, often granting broad, unmonitored access to sensitive data across departments. A custom HRMS engineered by TrustNet Security allows an enterprise to implement exact, least-privilege Role-Based Access Controls (RBAC), automated SCIM offboarding workflows, immutable audit logging, and custom data loss prevention filters tailored precisely to their organizational security policies.
What is the difference between Role-Based Access Control (RBAC) and Attribute-Based Access Control (ABAC)?
Role-Based Access Control (RBAC) assigns permissions based solely on an employee’s static organizational job title (e.g., “HR Manager”). Attribute-Based Access Control (ABAC) evaluates dynamic, multi-factor attributes at the exact moment of access, including the user’s role, their physical device health, network location, time of day, and the specific sensitivity rating of the requested file, providing vastly superior contextual security against insider exploitation.
