Enterprise B2B SaaS applications store massive volumes of confidential corporate data, making legacy password authentication a catastrophic liability for modern software vendors. Achieving enterprise-grade protection requires engineering seamless Single Sign-On (SSO) protocols like SAML 2.0 and OIDC combined with an uncompromising Zero Trust architecture—the gold standard of secure cloud engineering delivered by TrustNet Security.
When high-growth software-as-a-service (SaaS) companies transition from serving small businesses to closing six-figure enterprise contracts, their product roadmap hits an immediate architectural barrier. Enterprise Chief Information Security Officers (CISOs) and IT procurement teams will not permit their corporate employees to create independent usernames and passwords inside external third-party software. Managing isolated user accounts across dozens of disjointed SaaS tools introduces crippling password sprawl, increases vulnerability to phishing attacks, and makes rapid employee offboarding impossible.
To win and retain lucrative Fortune 500 and enterprise clients, B2B SaaS platforms must provide native, seamless enterprise authentication. However, simply checking an “SSO supported” box on a marketing landing page is insufficient. Modern enterprise security demands a holistic Zero Trust architecture where identity is verified continuously, session privilege is compartmentalized, and multi-tenant database infrastructure is mathematically isolated against unauthorized cross-tenant leakage.
The Evolution of SaaS Authentication: Why Passwords are Obsolete
Traditional password-based authentication was conceived for a simpler, decentralized internet. In the modern cloud ecosystem, relying on basic credentials introduces severe systemic vulnerabilities that threaten both SaaS vendors and their corporate customers.
According to global cybersecurity research, credential-based attacks account for over 80% of enterprise data breaches. When an employee reuses a corporate password across external consumer platforms, a breach on an unrelated website exposes their corporate SaaS access. Furthermore, when an employee resigns or is terminated, manual account deactivation across forty different SaaS tools is prone to human error, leaving dormant administrative access open for months.
Enterprise Single Sign-On (SSO) eliminates this danger by centralizing identity verification within the enterprise’s primary Identity Provider (IdP), such as Okta, Microsoft Azure Active Directory (Entra ID), Ping Identity, or Google Workspace. When an employee logs in, the SaaS application never handles, processes, or stores the user’s password; instead, it accepts cryptographically signed identity assertions directly from the trusted IdP.
Deconstructing SSO Standards: SAML 2.0 vs. OAuth 2.0 and OIDC
Engineering enterprise SaaS authentication requires selecting and implementing the appropriate cryptographic protocols. While multiple standards exist, enterprise software architects must master two primary frameworks.
1. SAML 2.0 (Security Assertion Markup Language)
SAML 2.0 remains the undisputed global heavyweight for enterprise-level B2B authentication. Operating on XML-based cryptographic assertions, SAML coordinates communication between the Identity Provider (IdP) and the Service Provider (SP, your SaaS application).
The SAML workflow operates through a multi-step cryptographic handshake:
- The user attempts to access your SaaS portal at
app.yourplatform.com. - Your portal generates an encoded SAML Authentication Request and redirects the user’s browser directly to their corporate IdP login portal.
- The user authenticates securely at the IdP via multi-factor biometrics or corporate hardware security keys.
- The IdP generates an XML SAML Response containing cryptographically signed user attributes (email, name, role, security groups) and posts it back to your Assertion Consumer Service (ACS) endpoint.
- Your SaaS backend verifies the digital signature using the IdP’s public X.509 certificate, establishes a secure user session, and grants access.
2. OpenID Connect (OIDC) and OAuth 2.0
While OAuth 2.0 is an authorization framework designed for granting third-party API permissions (such as allowing an app to access Google Calendar), OpenID Connect (OIDC) adds a standardized identity verification layer on top of OAuth 2.0 using lightweight JSON Web Tokens (JWTs).
OIDC is exceptionally well-suited for modern single-page applications (SPAs) built in React, Vue, or Angular, as well as native iOS and Android enterprise mobile apps. It utilizes RESTful API design patterns, produces smaller cryptographic payloads than bulky SAML XML documents, and integrates seamlessly with cloud-native microservices architectures.
The Zero Trust Paradigm: Never Trust, Always Verify
While Single Sign-On solves the challenge of initial user authentication, it does not guarantee continuous application security. Traditional perimeter security operated on a “castle-and-moat” philosophy: once a user passed authentication at the front gate, they were implicitly trusted throughout the entire internal network.
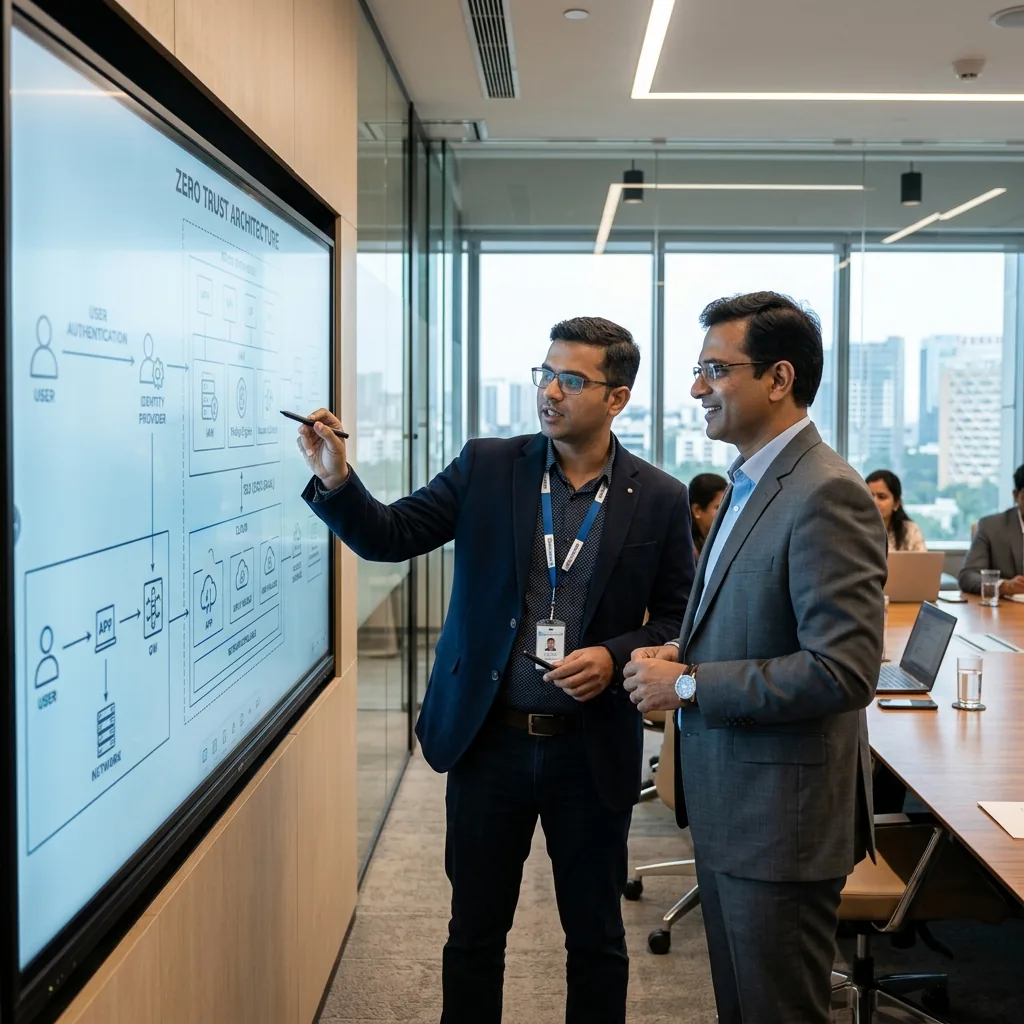
Zero Trust Architecture (ZTA) completely dismantles this outdated assumption. In a Zero Trust environment, no entity—whether an internal microservice, an enterprise executive, or an automated background worker—is ever granted implicit trust. Every single request must be authenticated, authorized, and cryptographically verified at every layer of the software stack.
1. Continuous Session Evaluation (Zero Trust Network Access)
Traditional web applications validate a user’s credentials once during initial login and generate a session token valid for 24 hours. If an attacker steals that session cookie via cross-site scripting (XSS) or a compromised browser extension, they enjoy unrestricted access until the token expires.
In a Zero Trust SaaS portal, sessions are evaluated dynamically and continuously. The application monitors context-aware telemetry including IP subnet shifts, device health compliance, and anomalous transaction velocity. If an administrative user suddenly initiates a bulk customer data export from an unrecognized IP address located in a foreign country, the Zero Trust policy engine immediately revokes the session token and forces an instantaneous out-of-band biometric challenge.
2. Micro-Segmentation and Least-Privilege Role-Based Access (RBAC)
Within an enterprise SaaS platform, administrative access must be strictly micro-segmented. Enterprise clients require granular role customization, ensuring that a “Billing Manager” can manage subscription invoices without viewing customer PII, and an “Auditor” can inspect system logs without modifying user configuration settings. Enforcing strict Principle of Least Privilege (PoLP) guarantees that even if a corporate credential is breached, the attacker’s lateral movement is severely restricted.
3. Multi-Tenant Cryptographic Isolation
In multi-tenant cloud software, hundreds of corporate enterprises share the same underlying database servers. A severe architectural flaw—such as an unauthenticated database query or broken object-level authorization (BOLA)—can result in Cross-Tenant Data Leakage, where Company A accidentally views the proprietary data of Company B.
Zero Trust SaaS portals implement rigorous logical and cryptographic isolation. Every database table query must be strictly bound to a tenant identifier parameter at the ORM layer. For high-tier enterprise clients in healthcare or financial services, leading SaaS platforms implement tenant-specific encryption keys stored in dedicated cloud Key Management Services (KMS), mathematically guaranteeing that data cannot be decrypted across tenant boundaries.
Automated Identity Provisioning: The Power of SCIM
Providing enterprise SSO is only half of the identity equation. Enterprise IT departments demand automated user lifecycle management. If an enterprise with 10,000 employees purchases your SaaS platform, their IT administrators cannot manually create 10,000 individual user accounts inside your settings panel.
This challenge is solved by implementing SCIM 2.0 (System for Cross-domain Identity Management). SCIM is an open standard HTTP-based protocol that allows corporate IdPs to automatically push real-time user provisioning and de-provisioning updates directly to your SaaS application.
- Instant Automated Onboarding: When a new employee joins the enterprise and is assigned to the appropriate department group in Okta or Azure AD, the IdP sends a SCIM API call that instantly creates their user account and provisions exact role permissions in your SaaS portal.
- Instant Automated Offboarding: The moment an employee departs the enterprise and their corporate directory profile is disabled, the IdP automatically transmits a SCIM termination request, instantly revoking all active sessions and deactivating their SaaS account within milliseconds, eliminating dormant account risk.
The Solution: TrustNet Security
Architecting enterprise-grade Single Sign-On, SCIM automated provisioning, and Zero Trust multi-tenant isolation requires elite software engineering and deep cryptographic expertise. Building these complex enterprise capabilities in-house with standard web developers frequently leads to severe authentication bypasses, broken session logic, and delayed enterprise sales cycles.
TrustNet Security is the premier Secure Web Development and enterprise software engineering agency. We specialize in transforming growing B2B SaaS platforms into hardened, enterprise-ready digital powerhouses:
- Custom Enterprise SSO Architecture: We architect and custom-code resilient SAML 2.0, OAuth 2.0, and OIDC integrations directly into your application stack, ensuring native, seamless compatibility with all major global enterprise IdPs (Okta, Azure AD, Ping, Google).
- Automated SCIM 2.0 Directory Sync: Our senior developers build robust, scalable SCIM microservices that handle high-volume automated user provisioning, group mapping, and real-time de-provisioning for enterprise clients.
- Zero Trust Multi-Tenant Engineering: We harden your backend database schemas, API gateways, and session management pipelines to enforce mathematical tenant isolation, attribute-based access controls, and dynamic anomaly detection.
- Full SOC 2 & ISO 27001 Readiness: We build your logging infrastructure, audit trails, and cryptographic key lifecycles to guarantee your SaaS application passes enterprise vendor security assessments with flying colors.
Win more six-figure enterprise contracts by proving your platform is engineered with impenetrable, bank-grade defense. Partner with TrustNet Security today to elevate your SaaS platform into an unassailable enterprise solution.
Frequently Asked Questions About Enterprise SaaS SSO and Zero Trust
Why do enterprise clients demand SAML SSO instead of Google/Social Login?
Enterprise organizations require total centralized control over corporate identity and access governance. Social login tools (like “Sign in with Google”) do not allow enterprise IT teams to enforce corporate password complexity, mandate hardware multi-factor authentication, apply conditional access network policies, or instantly revoke employee access upon termination. SAML SSO ties authentication directly into the corporate identity provider, giving enterprise IT complete administrative sovereignty.
What is the difference between SAML and SCIM?
SAML (Security Assertion Markup Language) is an authentication protocol that securely verifies a user’s identity and logs them into an application. SCIM (System for Cross-domain Identity Management) is a provisioning protocol that synchronizes user identity data (such as creating new accounts, updating job titles, assigning permission groups, and deleting departing employees) between the corporate directory and the SaaS platform automatically in the background.
Can a compromised session cookie bypass Multi-Factor Authentication?
Yes. If an attacker steals an active session token through cross-site scripting (XSS), malware, or session hijacking, they can inject that cookie directly into their own browser and impersonate the user without being prompted for a password or MFA code. This is why Zero Trust architecture is mandatory: by binding session tokens to device fingerprints, enforcing mutual TLS, and continually monitoring network telemetry, Zero Trust platforms detect anomalous token usage and terminate the session instantly.
How does Single Sign-On improve employee productivity?
Beyond massive security benefits, SSO drastically enhances operational efficiency. Employees no longer waste time creating, remembering, and frequently resetting dozens of complex passwords across multiple software tools. A single, highly secure daily authentication provides immediate, frictionless access to all authorized corporate applications, reducing corporate IT helpdesk password reset tickets by over 70%.
